 University of North Texas


PRISM Lab: Privacy First
Training models on local data, keeping it secure.
Privacy Aware & Intelligent System Modeling (PRISM) Lab
 Privacy Aware & Intelligent System Modeling (PRISM) Lab
University of North Texas
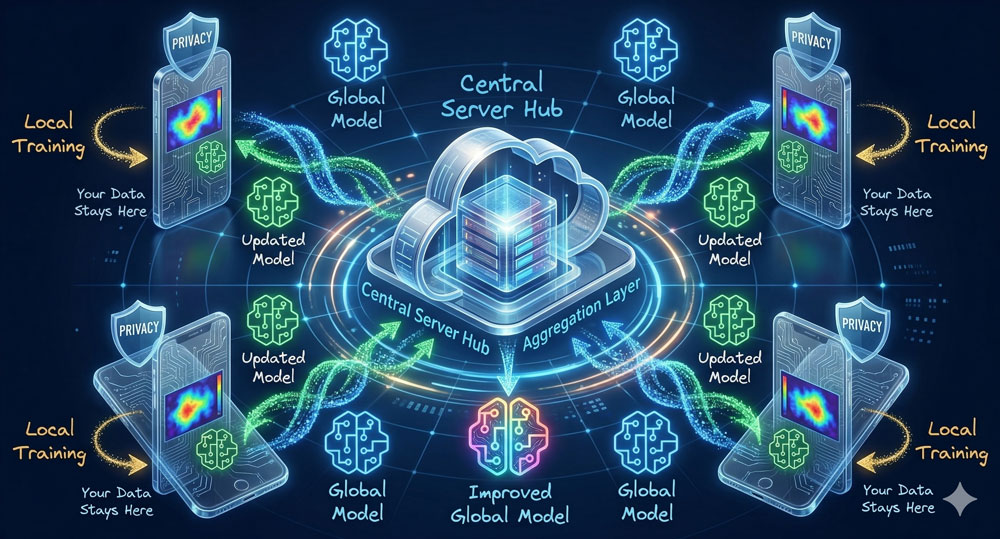
The PRISM Lab is focused on solving real-world challenges by developing privacy-preserving machine learning systems that are both secure and efficient. By leveraging federated learning and federated unlearning, we address the critical issue of data privacy in decentralized environments, enabling the training of models without the need to share raw data. This ensures sensitive information remains protected while still allowing for meaningful insights and predictions. Additionally, our federated unlearning techniques allow for the removal of specific data from models, ensuring data integrity without sacrificing model performance.
Our work on optimizing large language models (LLMs) addresses the practical need for more efficient, cost-effective AI systems. By integrating privacy-enhancing methods such as differential privacy and federated learning, we ensure user data remains secure while improving model accuracy and efficiency. We also explore advanced techniques like distillation, quantization, and pruning to reduce computational overhead and enhance model performance, making them more adaptable to low-resource settings and domains with limited data. Through these combined efforts, the PRISM Lab is solving key problems in AI, creating systems that are both scalable and privacy-conscious while delivering high-performing results across diverse applications.
Research Areas
Federated Learning/Unlearning
We design scalable unlearning protocols for decentralized learning systems so specific participants or samples can be removed while preserving utility, fairness, and communication efficiency.
We design scalable unlearning protocols for decentralized learning systems so specific participants or samples can be removed while preserving utility, fairness, and communication efficiency.
LLM Unlearning
Selective forgetting in large language models with minimal performance loss.
Our work studies data deletion and safety-driven removal in foundation models, combining efficient post-hoc unlearning strategies with robust evaluation to reduce residual memorization.
Cyber Security
Secure and privacy-preserving AI against poisoning, leakage, and model attacks.
We investigate adversarial and privacy threats in distributed ML, including data poisoning, model inversion, and gradient leakage, then build defense pipelines suitable for real deployments.
LLM Reasoning
Improving reasoning quality, robustness, and efficiency of language models.
The lab explores prompting, distillation, and alignment techniques that improve multi-step reasoning and reliability while lowering inference cost in domain-specific applications.
Announcements
Seeking PhD Students – Fall 2027
I am seeking highly motivated PhD students to join my lab in Fall 2026. As a professor leading cutting-edge research in Privacy-Enhanced Machine Learning, Federated Learning, Large Language Modeling, Visual Question Answering, Data Mining, Health Informatics, and Cybersecurity, I am committed to tackling complex challenges at the intersection of AI, privacy, and security. My lab focuses on interdisciplinary projects that aim to make a real-world impact. I am looking for passionate students, who are eager to contribute to innovative research and push the boundaries of these fields. If you're driven by curiosity and a desire to make a meaningful difference, I invite you to apply and join our collaborative research efforts.
Mission and Vision
The PRISM Lab envisions a future where high-performing AI can be used everywhere people need it most without requiring sensitive data to be collected, shared, or centralized. The lab aims to make privacy-preserving intelligence the norm in decentralized environments by enabling organizations and communities to benefit from robust predictions and decision support while keeping personal and proprietary information protected. PRISM also strives for AI systems that remain accountable over time, where models can be updated responsibly and data can be removed when required, so trust, compliance, and long-term integrity are built into the lifecycle of learning systems.
The PRISM Lab’s mission is to solve real-world problems by engineering machine learning systems that are secure, efficient, and practical to deploy at scale. The lab advances federated learning to train models across distributed data sources without exposing raw data and develops federated unlearning methods that support reliable data removal without degrading model utility. In parallel, PRISM focuses on making large language models more efficient and cost-effective by combining privacy-enhancing techniques such as differential privacy with model optimization approaches including distillation, quantization, and pruning. Through these efforts, the lab delivers scalable, privacy-conscious AI that performs strongly across diverse applications, including settings with limited compute, limited data, or strict privacy requirements.